
Email scams take many forms, from malware-ridden attachments supposedly sent by a friend to IRS impersonators and fake calendar invitations. Some use a spoofed email address to make a message appear to come from someone you trust, or even from your own address. Checking an email's full headers can help you spot this kind of impersonation, though it cannot tell you whether every message is safe.
Faking the visible “From” address does not require access to the real sender's account. A scammer can configure a sending server to put someone else's address in that field. Email providers use authentication checks and other filtering tools to detect these messages, and may reject them or send them to spam. But a spoofed message can still get through, and a legitimate message can end up in your spam folder.
The email header contains familiar information, such as From, To, Date, and Subject, along with technical details about how the message reached you. It can also contain the authentication results recorded by your email provider. Those results are useful clues about whether the visible sender's domain was authenticated, but they do not verify the identity of the individual who sent the email.
Scammers can also abuse legitimate email systems to send messages that pass authentication checks. For example, in a Robinhood phishing attack earlier this year, scammers injected a fake security warning into legitimate Robinhood emails. The messages came from Robinhood's real address and passed standard email security checks, yet directed recipients to a phishing site. Authentication can help detect a forged sender domain; it does not establish that an email's requests, links, or attachments are trustworthy.
How to find email header information
The steps vary depending on your email service or app. These instructions apply to desktop apps or webmail in a computer browser.
How to show email headers for Gmail
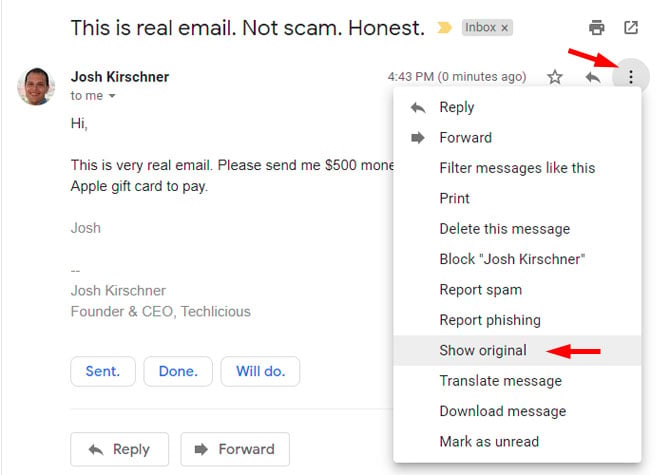
Open the email and click the three vertical dots next to the reply arrow, then select “Show original.” Gmail opens the full message headers and displays a summary of the SPF, DKIM, and DMARC authentication results.
How to show email headers for Outlook and Outlook.com
In classic Outlook for Windows, double-click the email to open it in its own window. Select File > Properties. The headers appear in the “Internet headers” box.
In new Outlook for Windows, Outlook.com, or Outlook on the web, open the email and select More actions (the three dots), then View > View message details.
How to show email headers for Proton Mail
In Proton Mail's web app, open the email and select More (the three dots) > View headers. The headers appear in a pop-up window, where you can download them as a text file.
You can also view headers in Proton Mail's iOS app. Open the message, tap the three dots at the top right, and select More options > View Headers.
How to show email headers for Apple Mail
In Apple Mail on a Mac, open the email and select View > Message > Raw Source to see the complete message source, including its headers. To display additional header fields within the message instead, select View > Message > All Headers.
How to show email headers for Yahoo Mail
Open the email, click More options (the three dots), and select “View Raw Message.” The message source, including its headers, opens in a new window or tab.
How to check an email's authentication results
Start with the authentication summary provided by your email service, if it displays one. Otherwise, look for an “Authentication-Results” field added by your receiving email provider. A message can contain several of these fields, including results from earlier servers, and attackers can insert fabricated ones. Do not assume that any line saying “pass” is your provider's verdict.
The three main checks are SPF, DKIM, and DMARC. Each checks a different part of the message's authentication, so you need to understand what a pass or failure actually means.
SPF checks whether a sending server is authorized
Sender Policy Framework (SPF) lets a domain specify which servers may send email using that domain in the SMTP envelope sender, an address used behind the scenes for mail delivery. This address can differ from the visible “From” address.
An SPF “pass” means the sending server was authorized for the domain being checked. It does not, by itself, authenticate the address you see in “From.” A scammer can pass SPF for a domain they control while displaying someone else's address as the sender.
An SPF “fail” means the domain's policy identifies the sending server as unauthorized. A “softfail” is a weaker indication that the server is probably unauthorized. Both deserve scrutiny, but neither proves fraud: forwarding and incorrect SPF settings can cause legitimate messages to fail. You may see these results in “Authentication-Results” or a separate “Received-SPF” field.
DKIM checks a domain's digital signature
DomainKeys Identified Mail (DKIM) verifies a digital signature associated with a domain and checks that the signed portions of the message have not changed. The signing domain may differ from the visible sender's domain, so a DKIM pass alone does not establish that the claimed sender sent the message.
DMARC connects authentication to the visible sender domain
Domain-based Message Authentication, Reporting, and Conformance (DMARC) checks whether a passing SPF or DKIM result uses a domain aligned with the domain in the visible “From” address. Depending on the domain's settings, alignment can allow related subdomains rather than requiring an exact match. DMARC also lets domain owners request how receiving providers handle messages that fail this check.
A DMARC “pass” means at least one of SPF or DKIM passed with an aligned domain. All three checks do not have to pass. This is a more useful check for spoofing of the visible sender domain than an SPF pass alone, but it still does not prove that a particular person sent the message or that its contents are safe.
A DMARC “fail” is a warning sign that the visible sender domain was not successfully authenticated through an aligned SPF or DKIM result. Forwarding, mailing lists, or configuration problems can also cause legitimate messages to fail. If a result is missing or says “none,” you do not have a successful DMARC check to rely on.
What the “Received” headers can tell you
Below is an example of a spoofed email I sent using an online spoofing service, pretending it came from my own address. The visible sender address looks right. Unless a different “Reply-To” address has been set, clicking Reply would ordinarily direct your response to the address shown in “From.” Scammers sometimes set a different Reply-To address to collect responses.
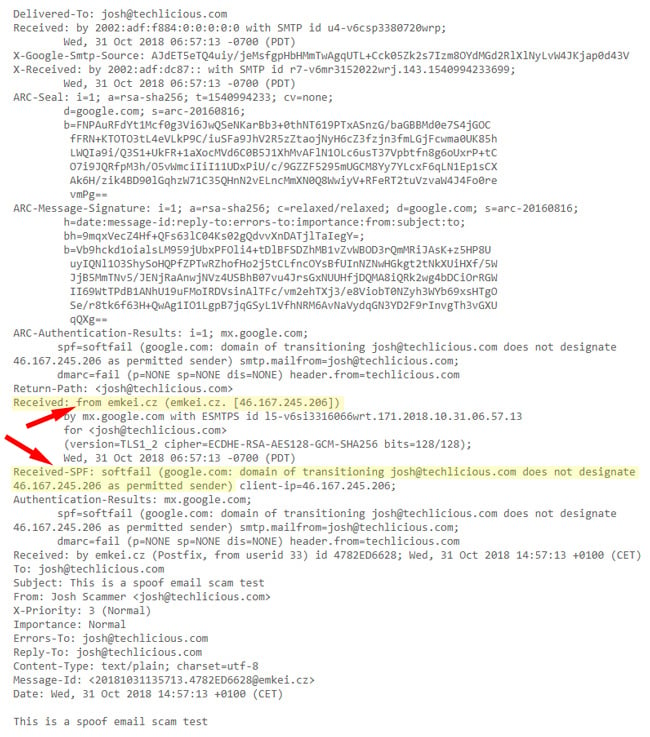
In this known spoofing example, the headers identify an emkei.cz server and show an SPF softfail. Those clues are consistent with how I sent the message. However, finding an unfamiliar server name in another email would not establish that it was spoofed.
“Received” entries normally record the servers that handled a message, with newer entries at the top. But a sender can insert fabricated entries before sending the email, so the bottommost entry is not automatically trustworthy. The useful starting point is an entry added by your trusted receiving provider that records which external server connected to it. Identifying that entry can require more technical knowledge than reading an authentication summary.
Legitimate companies often use outside services to send email, so the sending server's name does not need to match the domain in “From.” Looking up its IP address may provide information about the network or an approximate location, but it does not identify the person who sent the message. An unfamiliar provider or a server in another country is not proof of fraud.
What to do if an email seems suspicious
Use header information alongside what the message is asking you to do. Failed authentication deserves scrutiny, but a message that passes authentication can still be a scam sent from a compromised account, a lookalike domain, or an abused legitimate service.
If an email asks you to sign in, send money, share a verification code, or open an unexpected attachment, verify the request before acting. For a company, bank, or government agency, use its official app, a website you navigate to yourself, or a phone number from a statement or other trusted source. For a friend or colleague, contact them through a number or channel you already know. Avoid replying to the suspicious message or using the contact information it supplies.


From james on November 03, 2018 :: 5:55 pm
the list you show is not good for yahoo e-mail.
Reply
From Josh Kirschner on November 05, 2018 :: 3:27 pm
To see the email header info in Yahoo, open the email, click the three horizontal dots in the menu at the top of the message, and then hit “View raw message”
Reply
From Petah on March 25, 2021 :: 8:32 pm
does it mean its been hacked? received more emails while I was on phone to friend checking that they were not real. They do not show in his sent folder. I can’t block his address otherwise won’t receive his legitimate emails. what can he do? what can I do?
Reply
From Atherworld on March 24, 2026 :: 4:02 pm
What he can do is include a secret phrase in his e-mail to you, so if it doesn’t show up, it’s fake. Like Legity-git-git or such.